The best HWID spoofer in 2026 gives you a clean hardware fingerprint in minutes and a working path back into Fortnite, Valorant, Rust and Warzone
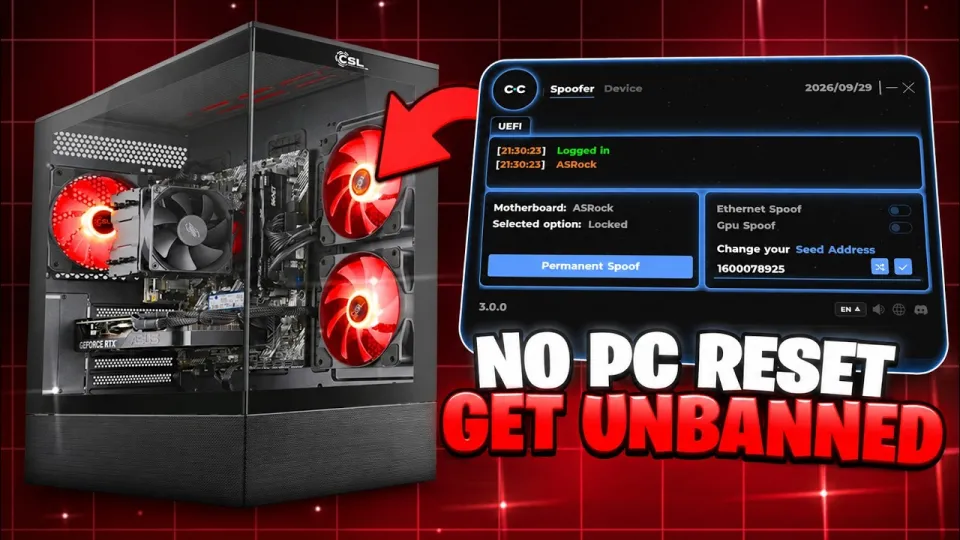
Video: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast
· based on the channel clixx
The best HWID spoofer is the one that changes every identifier a game uses to fingerprint your PC — motherboard and BIOS UUID, disk serials, network adapter MAC, SMBIOS strings and volume IDs — and does it cleanly enough that a fresh account is not flagged again on first launch. In practice that means a tool with a readable interface, per-component toggles and a clean uninstall path; the spoofer reviewed in the clixx tutorial is distributed through the Ceth Cheats store, where you can check current pricing and module support before committing.
An HWID (hardware ID) ban is not the same as an account ban. The anti-cheat records a fingerprint of your machine, so creating a new account on the same PC gets you removed again within minutes. Spoofing breaks that link by presenting different hardware values to the game client and, in the better tools, to the kernel-level driver that reads them.
What an HWID ban actually tracks and why a spoofer is needed
Anti-cheat systems build a composite fingerprint from several sources, and a ban record is tied to that composite rather than to a single serial. The usual components are the motherboard/BIOS UUID, SMBIOS and system manufacturer strings, the Windows machine GUID, physical disk serial numbers and volume IDs, the MAC address of each network adapter, and sometimes GPU and monitor EDID data. Because the fingerprint is a combination, changing one value is rarely enough — a partial spoof still leaves enough matching points for the ban to reattach.
That is why a dedicated hardware ID spoofer exists as a category. It rewrites the values in bulk, usually through a kernel driver that hooks the queries the anti-cheat makes, and it restores them when you unload the tool. Free "HWID changers" that only edit the registry machine GUID cover a fraction of what modern anti-cheats read, which is why they fail against Valorant's Vanguard or Rust's EAC-protected servers.
What the clixx spoofer tutorial covers
The video breakdown by clixx walks through the tool end to end: the interface layout, the available features, the configuration and settings screen, and the installation process. It is structured as an overview rather than a single click-to-fix demo, so you see what each toggle does before you run it — which matters, because a spoofer that changes the wrong disk serial can leave Windows unable to boot.
The supported game list shown with the tool spans Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant, plus a broader "and more" line. Those titles sit on different anti-cheat stacks — EAC and BattlEye on the Steam and Epic side, Vanguard on Valorant, Ricochet on Warzone — so compatibility is worth verifying per game rather than assuming one profile covers all of them.
How to set up a hardware ID spoofer step by step
Setup order matters more than any single setting, because a spoof applied after the game client starts is already too late. A safe sequence looks like this:
- Disable or fully exit the game and its launcher, then confirm the anti-cheat service is not running in the background.
- Create a Windows restore point or a full system image — serial changes touch boot-critical devices.
- Run the spoofer with administrator rights and select the components you need: disk, SMBIOS/motherboard, MAC address, and the registry identifiers.
- Apply the changes, then reboot. Most serial rewrites only take effect after a restart.
- Verify with a hardware info utility that the values actually changed before you launch anything.
- Start the game on a fresh account and check that no instant flag appears.
If the tool offers a temporary and a permanent mode, understand the difference: a temporary spoof reverts on reboot or when the driver unloads, while a permanent one writes the new identifiers to disk and survives restarts until you restore a backup. For a one-off unban check, temporary is lower risk; for a machine you intend to keep playing on, permanent is the practical choice.
Supported games and what to expect per anti-cheat
Compatibility is the single most common reason a spoofer "doesn't work", and it is almost always a mismatch between the tool's driver and the anti-cheat's detection surface. Fortnite and Rust run on Easy Anti-Cheat, which reads disk and SMBIOS data aggressively; CS2 and Rainbow Six Siege use different configurations of the same family; Apex Legends runs EAC as well; Warzone uses Ricochet, which leans heavily on kernel telemetry; Valorant's Vanguard is the strictest of the group and requires the spoof to be active before the driver loads at boot.
A few practical notes that apply across all of them: keep the spoofer version matched to your Windows build (major feature updates change the structures the driver patches), avoid running two spoofers at once, and re-apply after any large game patch that updates the anti-cheat module. FiveM is a separate case — its bans are server-side and tied to identifiers the client reports, so a client-side spoofer helps, but individual servers may add their own checks.
Risks, limits and how to judge a spoofer before buying
No spoofer is undetectable forever, and any vendor claiming otherwise is overselling. Anti-cheat teams actively look for the driver signatures and the tell-tale gaps a spoof leaves behind, so a tool that was clean last month can be flagged after the next update. Treat spoofing as a maintenance task, not a one-time purchase.
When evaluating a tool, check four things: whether it lists the specific components it rewrites, whether it ships a restore or backup function, whether updates are pushed after anti-cheat patches, and whether the vendor documents its refund terms. A clean interface and a settings screen — the parts the clixx tutorial spends most of its runtime on — are a good sign that the developer expects users to configure things deliberately rather than run a blind one-click script. Avoid anything requiring you to disable Windows security features permanently or to install a second, unexplained driver.
Where to get the tool and the links from the video
The software shown in the breakdown is sold through the vendor's own store, with a Discord server for support and update announcements. Both links from the video are below, copied exactly as published:
- Store and product page: https://cethcheats.cc/
- Community and support server: https://discord.gg/ceth
The video also includes a discount code, DENYS, for 5% off at checkout. Verify current game support on the store page before purchase, since the module list changes as anti-cheats update.
Bottom line on picking the best HWID spoofer
The best HWID spoofer for 2026 is the one that rewrites every identifier the anti-cheat reads — not just the registry GUID — and gives you a clean way back if something breaks. The clixx tutorial is a useful walkthrough of one such tool, covering its interface, configuration and installation rather than just a result, which is the right way to judge whether it fits your setup. Start with a restore point, spoof before the game launches, and re-check compatibility after every major anti-cheat patch. If you want to look at the tool from the video, head to the Ceth Cheats store and confirm the current game list and pricing first.
Key takeaways
- An HWID ban locks your motherboard, disk, NIC and other component serials to the ban record, so a new account alone does not get you back in.
- A spoofer rewrites those identifiers so the game client reports a different machine fingerprint on the next launch.
- The breakdown by channel clixx covers the tool's interface, configuration options and installation flow.
- Supported titles listed for the tool include Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant.
- The vendor store is cethcheats.cc, and the video includes a 5% coupon code: DENYS.
Questions & answers
Does an HWID spoofer actually get you unbanned?
It does not lift the ban — the ban record stays on the server. What it does is change the hardware fingerprint your PC reports, so a new account is not immediately matched to the old ban. Whether that works depends on how completely the tool rewrites the identifiers the specific anti-cheat reads.
Is a free HWID spoofer safe to use?
Free tools are usually limited to registry-level changes such as the machine GUID, which covers only a small part of a modern fingerprint, so they often fail. The bigger risk is that unsigned or repacked free spoofers frequently bundle unwanted drivers or stealers; if you use one, run it in a virtual machine first and never disable your security software permanently.
How long does a hardware ID spoof last?
A temporary spoof reverts on reboot or when the driver unloads, so it lasts for a single session. A permanent spoof writes the new serials to disk and survives restarts until you restore a backup or re-run the tool. Either way, the spoof can stop working after an anti-cheat update, so re-test after major patches.
Which games does the spoofer in the clixx tutorial support?
The supported list shown with the tool includes Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant, with a broader "and more" line. Because these titles run on different anti-cheat systems — EAC, BattlEye, Ricochet and Vanguard — check the store page for the current per-game module list before buying.
Source: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast · Markdown version